Control Channel SSL/Data channel negotiation Module. More...
#include "syshead.h"#include "win32.h"#include "error.h"#include "common.h"#include "socket.h"#include "misc.h"#include "fdmisc.h"#include "interval.h"#include "status.h"#include "gremlin.h"#include "pkcs11.h"#include "route.h"#include "tls_crypt.h"#include "crypto_epoch.h"#include "ssl.h"#include "ssl_verify.h"#include "ssl_backend.h"#include "ssl_ncp.h"#include "ssl_util.h"#include "auth_token.h"#include "mss.h"#include "dco.h"#include "options_string.h"#include "memdbg.h"#include "openvpn.h"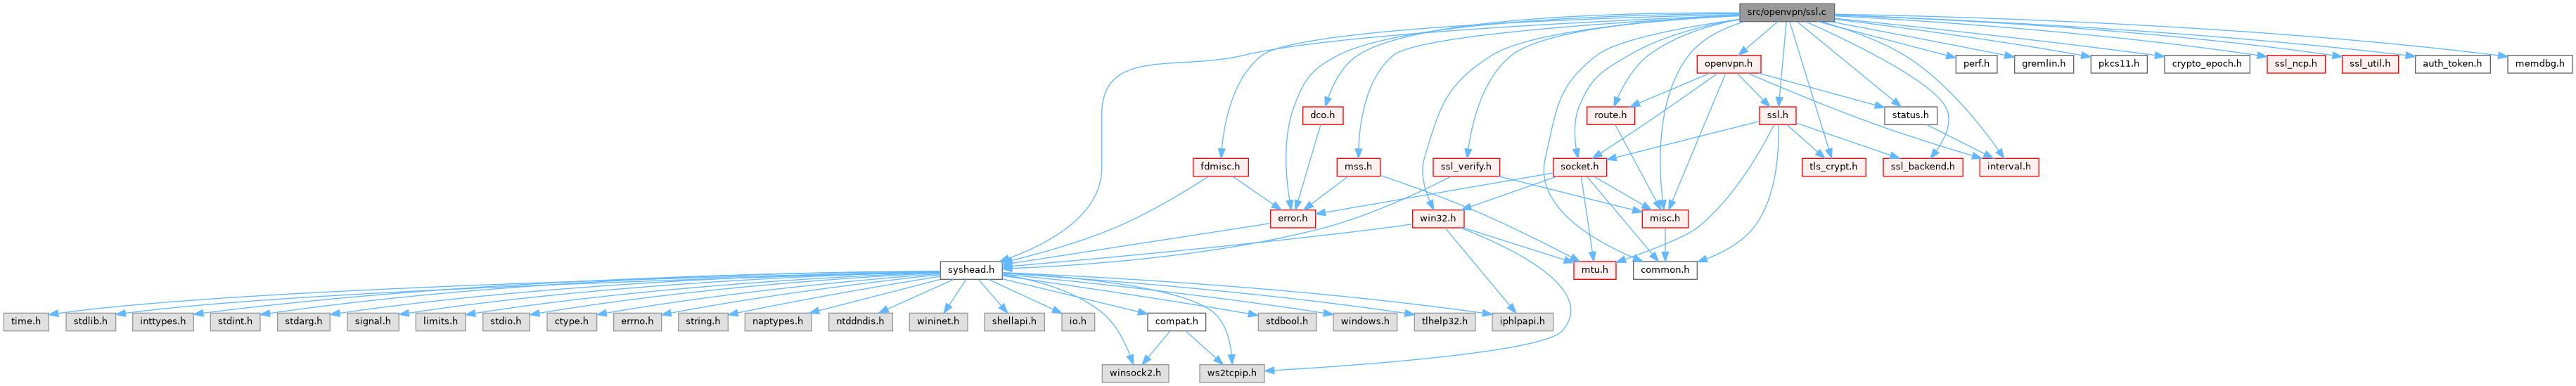
Go to the source code of this file.
Macros | |
| #define | INCR_SENT |
| #define | INCR_GENERATED |
| #define | INCR_SUCCESS |
| #define | INCR_ERROR |
Enumerations | |
| enum | key_gen_status { KEY_GEN_OK , KEY_GEN_FAILED , KEY_GEN_DCO_DESYNC } |
| Outcome of generating the data channel keys of a session. More... | |
Functions | |
| static void | check_session_buf_not_used (struct buffer *to_link, struct tls_session *session) |
| This is a safe guard function to double check that a buffer from a session is not used in a session to avoid a use after free. | |
| static void | check_keystate_buf_not_used (struct buffer *to_link, const struct key_state *ks) |
| static void | tls_limit_reneg_bytes (const char *ciphername, int64_t *reneg_bytes) |
| Limit the reneg_bytes value when using a small-block (<128 bytes) cipher. | |
| static uint64_t | tls_get_limit_aead (const char *ciphername) |
| void | tls_init_control_channel_frame_parameters (struct frame *frame, int tls_mtu) |
| static size_t | calc_control_channel_frame_overhead (const struct tls_session *session) |
| calculate the maximum overhead that control channel frames have This includes header, op code and everything apart from the payload itself. | |
| void | init_ssl_lib (void) |
| void | free_ssl_lib (void) |
| void | pem_password_setup (const char *auth_file) |
| int | pem_password_callback (char *buf, int size, int rwflag, void *u) |
| Callback to retrieve the user's password. | |
| void | enable_auth_user_pass (void) |
| void | auth_user_pass_setup (const char *auth_file, bool is_inline, bool username_only, const struct static_challenge_info *sci) |
| void | ssl_set_auth_nocache (void) |
| bool | ssl_get_auth_nocache (void) |
| void | ssl_set_auth_token (const char *token) |
| void | ssl_set_auth_token_user (const char *username) |
| bool | ssl_clean_auth_token (void) |
| void | ssl_purge_auth (const bool auth_user_pass_only) |
| void | ssl_purge_auth_challenge (void) |
| void | ssl_put_auth_challenge (const char *cr_str) |
| int | tls_version_parse (const char *vstr, const char *extra) |
| static void | tls_ctx_reload_crl (struct tls_root_ctx *ssl_ctx, const char *crl_file, bool crl_file_inline) |
| Load (or possibly reload) the CRL file into the SSL context. | |
| struct tls_root_ctx * | init_ssl (const struct options *options, bool in_chroot) |
| Build master SSL context object that serves for the whole of OpenVPN instantiation. | |
| static const char * | state_name (int state) |
| static const char * | ks_auth_name (enum ks_auth_state auth) |
| static const char * | session_index_name (int index) |
| static const char * | print_key_id (struct tls_multi *multi, struct gc_arena *gc) |
| bool | is_hard_reset_method2 (int op) |
| Given a key_method, return true if opcode represents the one of the hard_reset op codes for key-method 2. | |
| static bool | tls_session_user_pass_enabled (struct tls_session *session) |
| Returns whether or not the server should check for username/password. | |
| static void | move_session (struct tls_multi *multi, int dest, int src, bool reinit_src, struct buffer *to_link) |
| static void | reset_session (struct tls_multi *multi, struct tls_session *session, struct buffer *to_link) |
| static void | compute_earliest_wakeup (interval_t *earliest, time_t seconds_from_now) |
| static bool | lame_duck_must_die (const struct tls_session *session, interval_t *wakeup) |
| struct tls_multi * | tls_multi_init (struct tls_options *tls_options) |
Allocate and initialize a tls_multi structure. | |
| void | tls_multi_init_finalize (struct tls_multi *multi, int tls_mtu) |
Finalize initialization of a tls_multi structure. | |
| struct tls_auth_standalone * | tls_auth_standalone_init (struct tls_options *tls_options, struct gc_arena *gc) |
| void | tls_auth_standalone_free (struct tls_auth_standalone *tas) |
| Frees a standalone tls-auth verification object. | |
| void | tls_multi_init_set_options (struct tls_multi *multi, const char *local, const char *remote) |
| void | tls_multi_free (struct tls_multi *multi, bool clear) |
Cleanup a tls_multi structure and free associated memory allocations. | |
| static void | key_source_print (const struct key_source *k, const char *prefix) |
| static void | key_source2_print (const struct key_source2 *k) |
| static bool | openvpn_PRF (const uint8_t *secret, size_t secret_len, const char *label, const uint8_t *client_seed, size_t client_seed_len, const uint8_t *server_seed, size_t server_seed_len, const struct session_id *client_sid, const struct session_id *server_sid, uint8_t *output, size_t output_len) |
| static void | init_epoch_keys (struct key_state *ks, struct tls_multi *multi, const struct key_type *key_type, bool server, const struct key2 *key2) |
| static enum key_gen_status | init_key_contexts (struct key_state *ks, struct tls_multi *multi, const struct key_type *key_type, bool server, const struct key2 *key2, bool dco) |
| static bool | generate_key_expansion_tls_export (struct tls_session *session, struct key2 *key2) |
| static bool | generate_key_expansion_openvpn_prf (const struct tls_session *session, struct key2 *key2) |
| static enum key_gen_status | generate_key_expansion (struct tls_multi *multi, struct key_state *ks, struct tls_session *session) |
| static enum key_gen_status | tls_session_generate_data_channel_keys (struct tls_multi *multi, struct tls_session *session) |
| Generate data channel keys for the supplied TLS session. | |
| bool | tls_session_update_crypto_params_do_work (struct tls_multi *multi, struct tls_session *session, struct options *options, struct frame *frame, struct frame *frame_fragment, struct link_socket_info *lsi, dco_context_t *dco) |
| bool | tls_session_update_crypto_params (struct tls_multi *multi, struct tls_session *session, struct options *options, struct frame *frame, struct frame *frame_fragment, struct link_socket_info *lsi, dco_context_t *dco) |
| Update TLS session crypto parameters (cipher and auth) and derive data channel keys based on the supplied options. | |
| static bool | random_bytes_to_buf (struct buffer *buf, uint8_t *out, int outlen) |
| static bool | key_source2_randomize_write (struct key_source2 *k2, struct buffer *buf, bool server) |
| static int | key_source2_read (struct key_source2 *k2, struct buffer *buf, bool server) |
| static void | flush_payload_buffer (struct key_state *ks) |
| static void | key_state_soft_reset (struct tls_session *session, struct buffer *to_link) |
| void | tls_session_soft_reset (struct tls_multi *tls_multi) |
| static bool | write_empty_string (struct buffer *buf) |
| static bool | write_string (struct buffer *buf, const char *str, const int maxlen) |
| static int | read_string (struct buffer *buf, char *str, const unsigned int capacity) |
Read a string that is encoded as a 2 byte header with the length from the buffer buf. | |
| static char * | read_string_alloc (struct buffer *buf) |
| static bool | push_peer_info_peerid (struct buffer *out, struct tls_multi *multi, struct tls_session *session) |
| static bool | push_peer_info (struct buffer *buf, struct tls_multi *multi, struct tls_session *session) |
| Prepares the IV_ and UV_ variables that are part of the exchange to signal the peer's capabilities. | |
| static bool | key_method_2_write (struct buffer *buf, struct tls_multi *multi, struct tls_session *session) |
| Handle the writing of key data, peer-info, username/password, OCC to the TLS control channel (cleartext). | |
| static void | export_user_keying_material (struct tls_session *session) |
| static bool | key_method_2_read (struct buffer *buf, struct tls_multi *multi, struct tls_session *session) |
| Handle reading key data, peer-info, username/password, OCC from the TLS control channel (cleartext). | |
| static int | auth_deferred_expire_window (const struct tls_options *o) |
| static bool | session_move_pre_start (const struct tls_session *session, struct key_state *ks, bool skip_initial_send) |
| Move the session from S_INITIAL to S_PRE_START. | |
| static void | session_move_active (struct tls_multi *multi, struct tls_session *session, struct link_socket_info *to_link_socket_info, struct key_state *ks) |
| Moves the key to state to S_ACTIVE and also advances the multi_state state machine if this is the initial connection. | |
| bool | session_skip_to_pre_start (struct tls_session *session, struct tls_pre_decrypt_state *state, struct link_socket_actual *from) |
| static bool | parse_early_negotiation_tlvs (struct buffer *buf, const struct tls_session *session, struct key_state *ks) |
| Parses the TLVs (type, length, value) in the early negotiation. | |
| static bool | read_incoming_tls_ciphertext (struct buffer *buf, struct key_state *ks, bool *continue_tls_process) |
| Read incoming ciphertext and passes it to the buffer of the SSL library. | |
| static bool | control_packet_needs_wkc (const struct key_state *ks) |
| static bool | read_incoming_tls_plaintext (struct key_state *ks, struct buffer *buf, interval_t *wakeup, bool *continue_tls_process) |
| static bool | write_outgoing_tls_ciphertext (struct tls_session *session, bool *continue_tls_process) |
| static bool | check_outgoing_ciphertext (struct key_state *ks, struct tls_session *session, struct buffer *to_link, bool *continue_tls_process) |
| static bool | tls_process_state (struct tls_multi *multi, struct tls_session *session, struct buffer *to_link, struct link_socket_actual **to_link_addr, struct link_socket_info *to_link_socket_info, interval_t *wakeup) |
| static bool | should_trigger_renegotiation (const struct tls_session *session, const struct key_state *ks) |
| Determines if a renegotiation should be triggerred based on the various factors that can trigger one. | |
| static bool | tls_process (struct tls_multi *multi, struct tls_session *session, struct buffer *to_link, struct link_socket_actual **to_link_addr, struct link_socket_info *to_link_socket_info, interval_t *wakeup) |
| int | tls_multi_process (struct tls_multi *multi, struct buffer *to_link, struct link_socket_actual **to_link_addr, struct link_socket_info *to_link_socket_info, interval_t *wakeup) |
| static void | print_key_id_not_found_reason (struct tls_multi *multi, const struct link_socket_actual *from, int key_id) |
| We have not found a matching key to decrypt data channel packet, try to generate a sensible error message and print it. | |
| static void | handle_data_channel_packet (struct tls_multi *multi, const struct link_socket_actual *from, struct buffer *buf, struct crypto_options **opt, bool floated, const uint8_t **ad_start) |
Check the keyid of the an incoming data channel packet and return the matching crypto parameters in opt if found. | |
| bool | tls_pre_decrypt (struct tls_multi *multi, const struct link_socket_actual *from, struct buffer *buf, struct crypto_options **opt, bool floated, const uint8_t **ad_start) |
| Determine whether an incoming packet is a data channel or control channel packet, and process accordingly. | |
| struct key_state * | tls_select_encryption_key (struct tls_multi *multi) |
| Selects the primary encryption that should be used to encrypt data of an outgoing packet. | |
| void | tls_pre_encrypt (struct tls_multi *multi, struct buffer *buf, struct crypto_options **opt) |
| Choose the appropriate security parameters with which to process an outgoing packet. | |
| void | tls_prepend_opcode_v1 (const struct tls_multi *multi, struct buffer *buf) |
| Prepend a one-byte OpenVPN data channel P_DATA_V1 opcode to the packet. | |
| void | tls_prepend_opcode_v2 (const struct tls_multi *multi, struct buffer *buf) |
| Prepend an OpenVPN data channel P_DATA_V2 header to the packet. | |
| void | tls_post_encrypt (struct tls_multi *multi, struct buffer *buf) |
| Perform some accounting for the key state used. | |
| bool | tls_send_payload (struct key_state *ks, const uint8_t *data, size_t size) |
| bool | tls_rec_payload (struct tls_multi *multi, struct buffer *buf) |
| void | tls_update_remote_addr (struct tls_multi *multi, const struct link_socket_actual *addr) |
| Updates remote address in TLS sessions. | |
| void | show_available_tls_ciphers (const char *cipher_list, const char *cipher_list_tls13, const char *tls_cert_profile) |
| const char * | protocol_dump (struct buffer *buffer, unsigned int flags, struct gc_arena *gc) |
Functions for initialization and cleanup of key_state structures | |
| static void | key_state_init (struct tls_session *session, struct key_state *ks) |
Initialize a key_state structure. | |
| static void | key_state_free (struct key_state *ks, bool clear, struct buffer *to_link) |
Cleanup a key_state structure. | |
Functions for initialization and cleanup of tls_session structures | |
| static void | tls_session_init (struct tls_multi *multi, struct tls_session *session) |
Initialize a tls_session structure. | |
| static void | tls_session_free (struct tls_session *session, bool clear, struct buffer *to_link) |
Clean up a tls_session structure. | |
Variables | |
| static struct user_pass | passbuf |
| static bool | auth_user_pass_enabled |
| static struct user_pass | auth_user_pass |
| static struct user_pass | auth_token |
| static char * | auth_challenge |
Detailed Description
Control Channel SSL/Data channel negotiation Module.
Definition in file ssl.c.
Macro Definition Documentation
◆ INCR_ERROR
| #define INCR_ERROR |
Definition at line 95 of file ssl.c.
Referenced by tls_process_state().
◆ INCR_GENERATED
| #define INCR_GENERATED |
Definition at line 93 of file ssl.c.
Referenced by session_move_pre_start(), and write_outgoing_tls_ciphertext().
◆ INCR_SENT
| #define INCR_SENT |
Definition at line 92 of file ssl.c.
Referenced by tls_process_state().
◆ INCR_SUCCESS
| #define INCR_SUCCESS |
Definition at line 94 of file ssl.c.
Referenced by session_move_active().
Enumeration Type Documentation
◆ key_gen_status
| enum key_gen_status |
Outcome of generating the data channel keys of a session.
KEY_GEN_DCO_DESYNC is kept distinct from KEY_GEN_FAILED because it means userspace and kernel disagree about the DCO peer: the session cannot recover on its own and the connection has to be restarted, while any other failure only invalidates the affected key state.
| Enumerator | |
|---|---|
| KEY_GEN_OK | keys were generated and installed |
| KEY_GEN_FAILED | generation failed, invalidate the key state |
| KEY_GEN_DCO_DESYNC | the DCO peer is gone from the kernel |
Function Documentation
◆ auth_deferred_expire_window()
|
static |
Definition at line 2495 of file ssl.c.
References tls_options::handshake_window, and tls_options::renegotiate_seconds.
Referenced by session_move_pre_start().
◆ auth_user_pass_setup()
| void auth_user_pass_setup | ( | const char * | auth_file, |
| bool | is_inline, | ||
| bool | username_only, | ||
| const struct static_challenge_info * | sci ) |
Definition at line 302 of file ssl.c.
References auth_challenge, auth_token, auth_user_pass, static_challenge_info::challenge_text, static_challenge_info::flags, get_user_pass(), get_user_pass_cr(), GET_USER_PASS_DYNAMIC_CHALLENGE, GET_USER_PASS_INLINE_CREDS, GET_USER_PASS_MANAGEMENT, GET_USER_PASS_STATIC_CHALLENGE, GET_USER_PASS_STATIC_CHALLENGE_CONCAT, GET_USER_PASS_STATIC_CHALLENGE_ECHO, GET_USER_PASS_USERNAME_ONLY, SC_CONCAT, SC_ECHO, unprotect_user_pass(), and UP_TYPE_AUTH.
Referenced by init_query_passwords(), and key_method_2_write().
◆ calc_control_channel_frame_overhead()
|
static |
calculate the maximum overhead that control channel frames have This includes header, op code and everything apart from the payload itself.
This method is a bit pessimistic and might give higher overhead than we actually have
Definition at line 197 of file ssl.c.
References ACK_SIZE, CONTROL_SEND_ACK_MAX, datagram_overhead(), hmac_ctx_size(), session::key, KS_PRIMARY, reliable_ack::len, key_state::lru_acks, min_int(), packet_id_size(), PROTO_UDP, key_state::rec_ack, reliable_ack_outstanding(), SID_SIZE, and tls_crypt_buf_overhead().
Referenced by write_outgoing_tls_ciphertext().
◆ check_keystate_buf_not_used()
Definition at line 3266 of file ssl.c.
References key_state::ack_write_buf, reliable::array, reliable_entry::buf, buffer::data, key_state::key_id, buffer::len, M_FATAL, M_INFO, msg, S_UNDEF, key_state::send_reliable, reliable::size, key_state::state, and state_name().
Referenced by check_session_buf_not_used(), and key_state_free().
◆ check_outgoing_ciphertext()
|
static |
Definition at line 2831 of file ssl.c.
References D_TLS_DEBUG, dmsg, buffer::len, reliable_get_buf_output_sequenced(), S_START, key_state::send_reliable, key_state::state, and write_outgoing_tls_ciphertext().
Referenced by tls_process_state().
◆ check_session_buf_not_used()
|
static |
This is a safe guard function to double check that a buffer from a session is not used in a session to avoid a use after free.
- Parameters
-
to_link session
Definition at line 3323 of file ssl.c.
References check_keystate_buf_not_used(), buffer::data, session::key, KS_SIZE, buffer::len, M_INFO, and msg.
Referenced by move_session(), and tls_session_free().
◆ compute_earliest_wakeup()
|
inlinestatic |
Definition at line 1130 of file ssl.c.
Referenced by lame_duck_must_die(), and tls_process().
◆ control_packet_needs_wkc()
|
static |
Definition at line 2713 of file ssl.c.
References CO_RESEND_WKC, key_state::crypto_options, crypto_options::flags, reliable::packet_id, and key_state::send_reliable.
Referenced by tls_process(), and write_outgoing_tls_ciphertext().
◆ enable_auth_user_pass()
| void enable_auth_user_pass | ( | void | ) |
Definition at line 296 of file ssl.c.
References auth_user_pass_enabled.
Referenced by init_query_passwords().
◆ export_user_keying_material()
|
static |
Definition at line 2271 of file ssl.c.
References D_TLS_DEBUG_MED, dmsg, format_hex_ex(), gc, gc_free(), gc_malloc(), gc_new(), key_state_export_keying_material(), M_WARN, msg, secure_memzero(), setenv_del(), and setenv_str().
Referenced by key_method_2_read().
◆ flush_payload_buffer()
|
static |
Definition at line 1802 of file ssl.c.
References buffer_list_peek(), buffer_list_pop(), buffer::data, key_state_write_plaintext_const(), key_state::ks_ssl, buffer::len, and key_state::paybuf.
Referenced by session_move_active().
◆ free_ssl_lib()
| void free_ssl_lib | ( | void | ) |
Definition at line 242 of file ssl.c.
References crypto_uninit_lib(), and tls_free_lib().
Referenced by uninit_static().
◆ generate_key_expansion()
|
static |
Definition at line 1537 of file ssl.c.
References check_key(), CO_USE_TLS_KEY_MATERIAL_EXPORT, key_state::crypto_options, D_TLS_ERRORS, generate_key_expansion_openvpn_prf(), generate_key_expansion_tls_export(), init_key_contexts(), key2_print(), crypto_options::key_ctx_bi, KEY_GEN_FAILED, key2::keys, msg, and secure_memzero().
Referenced by tls_session_generate_data_channel_keys().
◆ generate_key_expansion_openvpn_prf()
|
static |
Definition at line 1493 of file ssl.c.
References key_source2::client, session::key, KEY_EXPANSION_ID, key_source2_print(), key_state::key_src, key2::keys, KS_PRIMARY, key2::n, openvpn_PRF(), key_source::pre_master, key_source::random1, key_source::random2, secure_memzero(), key_source2::server, and key_state::session_id_remote.
Referenced by generate_key_expansion().
◆ generate_key_expansion_tls_export()
|
static |
Definition at line 1479 of file ssl.c.
References EXPORT_KEY_DATA_LABEL, key_state_export_keying_material(), key2::keys, and key2::n.
Referenced by generate_key_expansion().
◆ handle_data_channel_packet()
|
inlinestatic |
Check the keyid of the an incoming data channel packet and return the matching crypto parameters in opt if found.
Also move the buf to the start of the encrypted data, skipping the opcode and peer id header and setting also set ad_start for AEAD ciphers to the start of the authenticated data.
Definition at line 3644 of file ssl.c.
References ASSERT, key_state::authenticated, BPTR, buf_advance(), key_state::crypto_options, D_TLS_ERRORS, D_TLS_KEYSELECT, dmsg, gc, gc_free(), gc_new(), get_key_scan(), key_ctx_bi::initialized, crypto_options::key_ctx_bi, key_state::key_id, KEY_SCAN_SIZE, KS_AUTH_TRUE, buffer::len, link_socket_actual_match(), msg, key_state::n_bytes, key_state::n_packets, tls_multi::n_soft_errors, P_DATA_V1, P_DATA_V2, P_KEY_ID_MASK, P_OPCODE_SHIFT, print_key_id_not_found_reason(), print_link_socket_actual(), key_state::remote_addr, S_GENERATED_KEYS, key_state::state, and tls_clear_error().
Referenced by tls_pre_decrypt().
◆ init_epoch_keys()
|
static |
Definition at line 1362 of file ssl.c.
References key::cipher, key_state::crypto_options, epoch_key::epoch, epoch_init_key_ctx(), epoch_key::epoch_key, key_direction_state::in_key, KEY_DIRECTION_INVERSE, KEY_DIRECTION_NORMAL, key_direction_state_init(), key2::keys, key_direction_state::out_key, and secure_memzero().
Referenced by init_key_contexts().
◆ init_key_contexts()
|
static |
Definition at line 1420 of file ssl.c.
References key_type::cipher, cipher_kt_mode_aead(), cipher_kt_name(), CLEAR, CO_EPOCH_DATA_KEY_FORMAT, tls_options::crypto_flags, key_state::crypto_options, D_TLS_ERRORS, key::hmac, init_epoch_keys(), init_key_ctx_bi(), init_key_dco_bi(), crypto_options::key_ctx_bi, KEY_DIRECTION_INVERSE, KEY_DIRECTION_NORMAL, KEY_GEN_DCO_DESYNC, KEY_GEN_FAILED, KEY_GEN_OK, M_FATAL, M_WARN, msg, and tls_multi::opt.
Referenced by generate_key_expansion().
◆ init_ssl()
| struct tls_root_ctx * init_ssl | ( | const struct options * | options, |
| bool | in_chroot ) |
Build master SSL context object that serves for the whole of OpenVPN instantiation.
Definition at line 525 of file ssl.c.
References ALLOC_OBJ_CLEAR, BSTR, options::ca_file, options::ca_file_inline, options::ca_path, options::cert_file, options::cert_file_inline, options::chroot_dir, options::cipher_list, options::cipher_list_tls13, options::crl_file, options::crl_file_inline, options::cryptoapi_cert, options::dh_file, options::dh_file_inline, options::ecdh_curve, options::extra_certs_file, options::extra_certs_file_inline, gc, gc_free(), gc_new(), key_is_external(), load_xkey_provider(), M_WARN, options::management_certificate, options::management_flags, management_query_cert(), MF_EXTERNAL_CERT, MF_EXTERNAL_KEY, msg, options::pkcs12_file, options::pkcs12_file_inline, prepend_dir(), options::priv_key_file, options::priv_key_file_inline, options::ssl_flags, SSLF_CRL_VERIFY_DIR, options::tls_cert_profile, tls_clear_error(), tls_ctx_check_cert_time(), tls_ctx_free(), tls_ctx_load_ca(), tls_ctx_load_cert_file(), tls_ctx_load_cryptoapi(), tls_ctx_load_dh_params(), tls_ctx_load_ecdh_params(), tls_ctx_load_extra_certs(), tls_ctx_load_pkcs12(), tls_ctx_load_priv_file(), tls_ctx_new(), tls_ctx_reload_crl(), tls_ctx_restrict_ciphers(), tls_ctx_restrict_ciphers_tls13(), tls_ctx_set_cert_profile(), tls_ctx_set_options(), tls_ctx_set_tls_groups(), tls_ctx_use_management_external_key(), options::tls_groups, and options::tls_server.
Referenced by do_init_crypto_tls_c1().
◆ init_ssl_lib()
| void init_ssl_lib | ( | void | ) |
Definition at line 234 of file ssl.c.
References crypto_init_lib(), and tls_init_lib().
Referenced by init_static().
◆ is_hard_reset_method2()
| bool is_hard_reset_method2 | ( | int | op | ) |
Given a key_method, return true if opcode represents the one of the hard_reset op codes for key-method 2.
Definition at line 788 of file ssl.c.
References P_CONTROL_HARD_RESET_CLIENT_V2, P_CONTROL_HARD_RESET_CLIENT_V3, and P_CONTROL_HARD_RESET_SERVER_V2.
Referenced by tls_pre_decrypt(), and tls_process_state().
◆ key_method_2_read()
|
static |
Handle reading key data, peer-info, username/password, OCC from the TLS control channel (cleartext).
Definition at line 2305 of file ssl.c.
References ALLOC_ARRAY_CLEAR_GC, ALLOC_OBJ_CLEAR_GC, auth_set_client_reason(), key_state::authenticated, buf_advance(), buf_clear(), buf_read_u8(), CLEAR, COMP_F_MIGRATE, D_PUSH, D_TLS_ERRORS, export_user_keying_material(), extract_asymmetric_peer_id(), gc, gc_free(), gc_new(), session::key, key_state::key_id, KEY_METHOD_MASK, key_source2_read(), key_state::key_src, KS_AUTH_FALSE, KS_AUTH_TRUE, KS_PRIMARY, buffer::len, MAX_PEER_ID, msg, tls_multi::opt, options_cmp_equal(), options_string_compat_lzo(), options_string_extract_option(), options_warning(), output_peer_info_env(), p2p_mode_ncp(), user_pass::password, tls_multi::peer_info, plugin_call(), plugin_defined(), read_string(), read_string_alloc(), tls_multi::remote_ciphername, tls_multi::remote_usescomp, tls_multi::rx_peer_id, secure_memzero(), setenv_del(), SSLF_AUTH_USER_PASS_OPTIONAL, string_alloc(), TLS_OPTIONS_LEN, tls_session_user_pass_enabled(), tls_multi::tx_peer_id, tls_multi::use_asymmetric_peer_id, tls_multi::use_peer_id, USER_PASS_LEN, user_pass::username, verify_final_auth_checks(), and verify_user_pass().
Referenced by tls_process_state().
◆ key_method_2_write()
|
static |
Handle the writing of key data, peer-info, username/password, OCC to the TLS control channel (cleartext).
Definition at line 2150 of file ssl.c.
References ASSERT, auth_token, auth_user_pass, auth_user_pass_enabled, auth_user_pass_setup(), buf_init, buf_write_u32(), buf_write_u8(), COMP_F_MIGRATE, D_TLS_ERRORS, session::key, key_state::key_id, KEY_METHOD_2, key_source2_randomize_write(), key_state::key_src, KS_PRIMARY, M_WARN, MODE_SERVER, msg, tls_multi::opt, p2p_mode_ncp(), user_pass::password, protect_user_pass(), purge_user_pass(), push_peer_info(), tls_multi::remote_usescomp, secure_memzero(), strncpynt(), TLS_OPTIONS_LEN, unprotect_user_pass(), USER_PASS_LEN, user_pass::username, write_empty_string(), and write_string().
Referenced by tls_process_state().
◆ key_source2_print()
|
static |
Definition at line 1321 of file ssl.c.
References key_source2::client, key_source_print(), and key_source2::server.
Referenced by generate_key_expansion_openvpn_prf().
◆ key_source2_randomize_write()
|
static |
Definition at line 1739 of file ssl.c.
References CLEAR, key_source2::client, key_source::pre_master, key_source::random1, key_source::random2, random_bytes_to_buf(), and key_source2::server.
Referenced by key_method_2_write().
◆ key_source2_read()
|
static |
Definition at line 1770 of file ssl.c.
References buf_read(), CLEAR, key_source2::client, key_source::pre_master, key_source::random1, key_source::random2, and key_source2::server.
Referenced by key_method_2_read().
◆ key_source_print()
|
static |
Definition at line 1302 of file ssl.c.
References D_SHOW_KEY_SOURCE, dmsg, format_hex(), gc, gc_free(), gc_new(), key_source::pre_master, key_source::random1, key_source::random2, and VALGRIND_MAKE_READABLE.
Referenced by key_source2_print().
◆ key_state_soft_reset()
|
static |
Definition at line 1818 of file ssl.c.
References session::key, key_state_free(), key_state_init(), KS_LAME_DUCK, KS_PRIMARY, key_state::must_die, now, key_state::remote_addr, and key_state::session_id_remote.
Referenced by tls_pre_decrypt(), tls_process(), and tls_session_soft_reset().
◆ ks_auth_name()
|
static |
Definition at line 731 of file ssl.c.
References KS_AUTH_DEFERRED, KS_AUTH_FALSE, and KS_AUTH_TRUE.
Referenced by print_key_id().
◆ lame_duck_must_die()
|
inlinestatic |
Definition at line 1147 of file ssl.c.
References ASSERT, compute_earliest_wakeup(), session::key, KS_LAME_DUCK, key_state::must_die, now, S_ERROR, S_INITIAL, and key_state::state.
Referenced by tls_multi_process(), and tls_process().
◆ move_session()
|
static |
Definition at line 1094 of file ssl.c.
References ASSERT, check_session_buf_not_used(), D_TLS_DEBUG, D_TLS_DEBUG_LOW, dmsg, msg, secure_memzero(), tls_multi::session, session_index_name(), tls_session_free(), tls_session_init(), and TM_SIZE.
Referenced by tls_multi_process().
◆ openvpn_PRF()
|
static |
Definition at line 1328 of file ssl.c.
References alloc_buf(), ASSERT, BLENZ, BPTR, buf_clear(), buf_write(), free_buf(), session_id::id, SID_SIZE, ssl_tls1_PRF(), and VALGRIND_MAKE_READABLE.
Referenced by generate_key_expansion_openvpn_prf().
◆ parse_early_negotiation_tlvs()
|
static |
Parses the TLVs (type, length, value) in the early negotiation.
Definition at line 2627 of file ssl.c.
References buf_advance(), buf_len(), buf_read_u16(), CO_RESEND_WKC, key_state::crypto_options, D_TLS_ERRORS, EARLY_NEG_FLAG_RESEND_WKC, crypto_options::flags, buffer::len, msg, key_state::rec_reliable, reliable_mark_deleted(), and TLV_TYPE_EARLY_NEG_FLAGS.
Referenced by tls_process_state().
◆ pem_password_callback()
| int pem_password_callback | ( | char * | buf, |
| int | size, | ||
| int | rwflag, | ||
| void * | u ) |
Callback to retrieve the user's password.
- Parameters
-
buf Buffer to return the password in size Size of the buffer rwflag Unused, needed for OpenSSL compatibility u Unused, needed for OpenSSL compatibility
Definition at line 268 of file ssl.c.
References ASSERT, passbuf, pem_password_setup(), purge_user_pass(), and strncpynt().
Referenced by tls_ctx_load_pkcs12(), and tls_ctx_set_options().
◆ pem_password_setup()
| void pem_password_setup | ( | const char * | auth_file | ) |
Definition at line 257 of file ssl.c.
References get_user_pass(), GET_USER_PASS_MANAGEMENT, GET_USER_PASS_PASSWORD_ONLY, passbuf, unprotect_user_pass(), and UP_TYPE_PRIVATE_KEY.
Referenced by init_query_passwords(), and pem_password_callback().
◆ print_key_id()
Definition at line 772 of file ssl.c.
References alloc_buf_gc(), key_state::authenticated, BSTR, buf_printf(), gc, get_key_scan(), key_state::key_id, KEY_SCAN_SIZE, ks_auth_name(), session_id_print(), key_state::session_id_remote, key_state::state, and state_name().
Referenced by print_key_id_not_found_reason(), tls_pre_decrypt(), and tls_pre_encrypt().
◆ print_key_id_not_found_reason()
|
static |
We have not found a matching key to decrypt data channel packet, try to generate a sensible error message and print it.
Definition at line 3596 of file ssl.c.
References key_state::authenticated, D_MULTI_DROPPED, D_TLS_ERRORS, gc, gc_free(), gc_new(), get_key_scan(), key_state::key_id, KEY_SCAN_SIZE, KS_AUTH_DEFERRED, KS_AUTH_TRUE, msg, print_key_id(), print_link_socket_actual(), S_ACTIVE, S_GENERATED_KEYS, S_INITIAL, and key_state::state.
Referenced by handle_data_channel_packet().
◆ protocol_dump()
Definition at line 4327 of file ssl.c.
References alloc_buf_gc(), ASSERT, BLEN, BPTR, BSTR, buf_printf(), buf_read(), format_hex(), gc, buffer::len, MAX_HMAC_KEY_LENGTH, ntohpid, P_ACK_V1, P_DATA_V1, P_DATA_V2, P_KEY_ID_MASK, P_OPCODE_SHIFT, packet_id_format, packet_id_net_print(), packet_id_read(), packet_opcode_name(), PD_SHOW_DATA, PD_TLS, PD_TLS_AUTH_HMAC_SIZE_MASK, PD_TLS_CRYPT, PD_VERBOSE, reliable_ack_print(), session_id_print(), session_id_read(), and TLS_CRYPT_TAG_SIZE.
◆ push_peer_info()
|
static |
Prepares the IV_ and UV_ variables that are part of the exchange to signal the peer's capabilities.
The amount of variables is determined by session->opt->push_peer_info_detail
0     nothing. Used on a TLS P2MP server side to send no information
      to the client
1     minimal info needed for NCP in P2P mode
2     when --pull is enabled, the "default" set of variables
3     all information including MAC address and library versions
- Parameters
-
buf the buffer to write these variables to session the TLS session object multi the TLS multi object
- Returns
- true if no error was encountered
Definition at line 1958 of file ssl.c.
References alloc_buf_gc(), BLEN, BSTR, buf_printf(), buf_safe(), route_gateway_info::flags, format_hex_ex(), gc, gc_free(), gc_new(), get_default_gateway(), get_ssl_library_version(), route_gateway_info::hwaddr, IV_PROTO_AUTH_FAIL_TEMP, IV_PROTO_AUTH_PENDING_KW, IV_PROTO_CC_EXIT_NOTIFY, IV_PROTO_DATA_EPOCH, IV_PROTO_DATA_V2, IV_PROTO_DNS_OPTION_V2, IV_PROTO_DYN_TLS_CRYPT, IV_PROTO_NCP_P2P, IV_PROTO_PUSH_UPDATE, IV_PROTO_REQUEST_PUSH, IV_PROTO_TLS_KEY_EXPORT, env_set::list, MODE_SERVER, env_item::next, push_peer_info_peerid(), RGI_HWADDR_DEFINED, tls_item_in_cipher_list(), win32_version_string(), write_empty_string(), and write_string().
Referenced by key_method_2_write(), options_postprocess_verify_ce(), and show_settings().
◆ push_peer_info_peerid()
|
static |
Definition at line 1923 of file ssl.c.
References buf_printf(), MAX_PEER_ID, MODE_SERVER, tls_multi::rx_peer_id, and tls_multi::use_asymmetric_peer_id.
Referenced by push_peer_info().
◆ random_bytes_to_buf()
|
static |
Definition at line 1724 of file ssl.c.
References buf_write(), M_FATAL, msg, and rand_bytes().
Referenced by key_source2_randomize_write().
◆ read_incoming_tls_ciphertext()
|
static |
Read incoming ciphertext and passes it to the buffer of the SSL library.
Returns false if an error is encountered that should abort the session.
Definition at line 2687 of file ssl.c.
References D_TLS_DEBUG, D_TLS_ERRORS, dmsg, key_state_write_ciphertext(), key_state::ks_ssl, buffer::len, msg, key_state::rec_reliable, reliable_mark_deleted(), and status.
Referenced by tls_process_state().
◆ read_incoming_tls_plaintext()
|
static |
Definition at line 2720 of file ssl.c.
References ASSERT, buf_init, D_TLS_DEBUG, D_TLS_ERRORS, dmsg, key_state_read_plaintext(), key_state::ks_ssl, msg, status, and update_time().
Referenced by tls_process_state().
◆ read_string()
|
static |
Read a string that is encoded as a 2 byte header with the length from the buffer buf.
Will return the non-negative value if reading was successful. The returned value will include the trailing 0 byte.
If the message is over the capacity or could not be read it will return the negative length that was in the header and try to skip the string. If the string cannot be skipped, the buf will stay at the current position or position + 2
Definition at line 1883 of file ssl.c.
References buf_advance(), buf_read(), and buf_read_u16().
Referenced by key_method_2_read().
◆ read_string_alloc()
|
static |
Definition at line 1902 of file ssl.c.
References buf_read(), buf_read_u16(), and check_malloc_return().
Referenced by key_method_2_read().
◆ reset_session()
|
static |
Definition at line 1119 of file ssl.c.
References tls_session_free(), and tls_session_init().
Referenced by tls_multi_process().
◆ session_index_name()
|
static |
Definition at line 750 of file ssl.c.
References TM_ACTIVE, TM_INITIAL, and TM_LAME_DUCK.
Referenced by move_session().
◆ session_move_active()
|
static |
Moves the key to state to S_ACTIVE and also advances the multi_state state machine if this is the initial connection.
Definition at line 2559 of file ssl.c.
References CAS_NOT_CONNECTED, CAS_WAITING_AUTH, CAS_WAITING_OPTIONS_IMPORT, check_debug_level(), D_HANDSHAKE, D_TLS_DEBUG_MED, dmsg, key_state::established, flush_payload_buffer(), INCR_SUCCESS, key_state::ks_ssl, link_socket_set_outgoing_addr(), MODE_SERVER, tls_multi::multi_state, key_state::must_negotiate, now, print_details(), key_state::remote_addr, S_ACTIVE, and key_state::state.
Referenced by tls_process_state().
◆ session_move_pre_start()
|
static |
Move the session from S_INITIAL to S_PRE_START.
This will also generate the initial message based on ks->initial_opcode
- Returns
- if the state change was succesful
Definition at line 2514 of file ssl.c.
References key_state::auth_deferred_expire, auth_deferred_expire_window(), D_TLS_DEBUG, dmsg, gc, gc_free(), gc_new(), INCR_GENERATED, key_state::initial, key_state::initial_opcode, management_set_state(), key_state::must_negotiate, now, OPENVPN_STATE_WAIT, P_CONTROL_SOFT_RESET_V1, reliable_get_buf_output_sequenced(), reliable_mark_active_outgoing(), reliable_mark_deleted(), S_PRE_START, S_PRE_START_SKIP, key_state::send_reliable, session_id_print(), and key_state::state.
Referenced by session_skip_to_pre_start(), and tls_process_state().
◆ session_skip_to_pre_start()
| bool session_skip_to_pre_start | ( | struct tls_session * | session, |
| struct tls_pre_decrypt_state * | state, | ||
| struct link_socket_actual * | from ) |
Definition at line 2602 of file ssl.c.
References session::key, KS_PRIMARY, reliable::packet_id, key_state::rec_reliable, key_state::remote_addr, key_state::session_id_remote, session_move_pre_start(), and key_state::state.
Referenced by handle_connection_attempt().
◆ should_trigger_renegotiation()
|
static |
Determines if a renegotiation should be triggerred based on the various factors that can trigger one.
Definition at line 3053 of file ssl.c.
References aead_usage_limit_reached(), cipher_decrypt_verify_fail_warn(), CO_EPOCH_DATA_KEY_FORMAT, key_state::crypto_options, key_ctx_bi::decrypt, key_ctx_bi::encrypt, epoch_key::epoch, crypto_options::epoch_key_send, key_state::established, crypto_options::flags, packet_id_rec::id, packet_id_send::id, crypto_options::key_ctx_bi, key_state::n_bytes, key_state::n_packets, now, crypto_options::packet_id, packet_id_close_to_wrapping(), packet_id::rec, and packet_id::send.
Referenced by tls_process().
◆ show_available_tls_ciphers()
| void show_available_tls_ciphers | ( | const char * | cipher_list, |
| const char * | cipher_list_tls13, | ||
| const char * | tls_cert_profile ) |
Definition at line 4302 of file ssl.c.
References show_available_tls_ciphers_list(), TLS_VER_1_3, and tls_version_max().
Referenced by print_openssl_info().
◆ ssl_clean_auth_token()
| bool ssl_clean_auth_token | ( | void | ) |
Definition at line 384 of file ssl.c.
References auth_token, and purge_user_pass().
Referenced by man_forget_passwords(), man_reset_client_socket(), and receive_auth_failed().
◆ ssl_get_auth_nocache()
| bool ssl_get_auth_nocache | ( | void | ) |
Definition at line 360 of file ssl.c.
References passbuf.
Referenced by options_postprocess_mutate_ce().
◆ ssl_purge_auth()
| void ssl_purge_auth | ( | const bool | auth_user_pass_only | ) |
Definition at line 395 of file ssl.c.
References auth_user_pass, passbuf, purge_user_pass(), and ssl_purge_auth_challenge().
Referenced by do_init_crypto_tls_c1(), man_forget_passwords(), man_reset_client_socket(), receive_auth_failed(), and server_pushed_signal().
◆ ssl_purge_auth_challenge()
| void ssl_purge_auth_challenge | ( | void | ) |
Definition at line 413 of file ssl.c.
References auth_challenge.
Referenced by ssl_purge_auth(), and ssl_put_auth_challenge().
◆ ssl_put_auth_challenge()
| void ssl_put_auth_challenge | ( | const char * | cr_str | ) |
Definition at line 420 of file ssl.c.
References auth_challenge, ssl_purge_auth_challenge(), and string_alloc().
Referenced by receive_auth_failed().
◆ ssl_set_auth_nocache()
| void ssl_set_auth_nocache | ( | void | ) |
Definition at line 350 of file ssl.c.
References auth_user_pass, and passbuf.
Referenced by add_option().
◆ ssl_set_auth_token()
| void ssl_set_auth_token | ( | const char * | token | ) |
Definition at line 369 of file ssl.c.
References auth_token, and set_auth_token().
Referenced by add_option().
◆ ssl_set_auth_token_user()
| void ssl_set_auth_token_user | ( | const char * | username | ) |
Definition at line 375 of file ssl.c.
References auth_token, set_auth_token_user(), and user_pass::username.
Referenced by add_option().
◆ state_name()
|
static |
Definition at line 688 of file ssl.c.
References S_ACTIVE, S_ERROR, S_ERROR_PRE, S_GENERATED_KEYS, S_GOT_KEY, S_INITIAL, S_PRE_START, S_PRE_START_SKIP, S_SENT_KEY, S_START, and S_UNDEF.
Referenced by check_keystate_buf_not_used(), print_key_id(), tls_multi_process(), tls_pre_decrypt(), and tls_process().
◆ tls_ctx_reload_crl()
|
static |
Load (or possibly reload) the CRL file into the SSL context.
No reload is performed under the following conditions:
- the CRL file was passed inline
- the CRL file was not modified since the last (re)load
- Parameters
-
ssl_ctx The TLS context to use when reloading the CRL crl_file The file name to load the CRL from, or or an array containing the inline CRL. crl_file_inline True if crl_file is an inline CRL.
Definition at line 475 of file ssl.c.
References backend_tls_ctx_reload_crl(), tls_root_ctx::crl_last_mtime, tls_root_ctx::crl_last_size, M_FATAL, M_WARN, msg, and platform_stat().
Referenced by init_ssl(), and key_state_init().
◆ tls_get_limit_aead()
|
static |
Definition at line 129 of file ssl.c.
References cipher_get_aead_limits(), D_SHOW_KEYS, and msg.
Referenced by tls_session_generate_data_channel_keys().
◆ tls_limit_reneg_bytes()
|
static |
Limit the reneg_bytes value when using a small-block (<128 bytes) cipher.
- Parameters
-
ciphername The current cipher (may be NULL). reneg_bytes Pointer to the current reneg_bytes, updated if needed. May not be NULL.
Definition at line 115 of file ssl.c.
References cipher_kt_insecure(), M_WARN, and msg.
Referenced by tls_session_generate_data_channel_keys().
◆ tls_multi_process()
| int tls_multi_process | ( | struct tls_multi * | multi, |
| struct buffer * | to_link, | ||
| struct link_socket_actual ** | to_link_addr, | ||
| struct link_socket_info * | to_link_socket_info, | ||
| interval_t * | wakeup ) |
Definition at line 3365 of file ssl.c.
References link_socket_addr::actual, key_state::authenticated, CAS_CONNECT_DONE, CAS_PENDING, CAS_RECONNECT_PENDING, CAS_WAITING_AUTH, D_TLS_DEBUG, D_TLS_DEBUG_LOW, D_TLS_ERRORS, dmsg, gc, gc_free(), gc_new(), get_key_scan(), get_primary_key(), tls_options::gremlin, session::key, tls_session::key, KEY_GEN_DCO_DESYNC, KEY_GEN_OK, KEY_SCAN_SIZE, key_state_ssl_shutdown(), KS_AUTH_FALSE, KS_AUTH_TRUE, KS_LAME_DUCK, KS_PRIMARY, key_state::ks_ssl, lame_duck_must_die(), link_socket_actual_defined(), link_socket_info::lsa, move_session(), msg, tls_multi::multi_state, tls_multi::n_hard_errors, tls_multi::n_soft_errors, tls_multi::opt, print_link_socket_actual(), key_state::remote_addr, resend_auth_token_renegotiation(), reset_session(), S_ACTIVE, S_ERROR, S_ERROR_PRE, S_GENERATED_KEYS, S_INITIAL, tls_multi::session, session_id_print(), key_state::session_id_remote, tls_options::single_session, key_state::state, state_name(), status, TLS_AUTHENTICATED, TLS_AUTHENTICATION_FAILED, tls_authentication_status(), TLS_AUTHENTICATION_SUCCEEDED, tls_clear_error(), tls_process(), tls_session_free(), tls_session_generate_data_channel_keys(), TLSMP_ACTIVE, TLSMP_INACTIVE, TLSMP_KILL, TLSMP_RECONNECT, TLSMP_RESTART, TM_ACTIVE, TM_INITIAL, TM_LAME_DUCK, TM_SIZE, tls_multi::to_link_addr, and update_time().
Referenced by check_tls().
◆ tls_process()
|
static |
Definition at line 3141 of file ssl.c.
References key_state::ack_write_buf, ASSERT, frame::buf, buf_init, compute_earliest_wakeup(), control_packet_needs_wkc(), counter_format, key_state::crypto_options, D_TLS_DEBUG, D_TLS_DEBUG_LOW, key_ctx_bi::decrypt, dmsg, key_ctx_bi::encrypt, key_state::established, tls_options::frame, frame::headroom, session::key, crypto_options::key_ctx_bi, key_state_free(), key_state_soft_reset(), KS_LAME_DUCK, KS_PRIMARY, lame_duck_must_die(), buffer::len, msg, key_state::must_negotiate, key_state::n_bytes, key_state::n_packets, now, tls_multi::opt, P_ACK_V1, P_CONTROL_WKC_V1, key_ctx::plaintext_blocks, key_state::rec_ack, reliable_ack_empty(), RELIABLE_ACK_SIZE, reliable_get_buf_output_sequenced(), reliable_mark_active_outgoing(), reliable_send_timeout(), S_ERROR, S_ERROR_PRE, S_GENERATED_KEYS, S_INITIAL, S_UNDEF, key_state::send_reliable, session_id_defined(), should_trigger_renegotiation(), key_state::state, state_name(), tls_process_state(), update_time(), and write_control_auth().
Referenced by tls_multi_process().
◆ tls_process_state()
|
static |
Definition at line 2857 of file ssl.c.
References ASSERT, reliable_entry::buf, check_outgoing_ciphertext(), CONTROL_SEND_ACK_MAX, D_TLS_DEBUG, D_TLS_DEBUG_MED, D_TLS_ERRORS, dmsg, INCR_ERROR, INCR_SENT, is_hard_reset_method2(), session::key, key_method_2_read(), key_method_2_write(), key_state_ssl_shutdown(), key_state_write_plaintext(), KS_PRIMARY, key_state::ks_ssl, buffer::len, msg, key_state::must_negotiate, now, reliable_entry::opcode, reliable_entry::packet_id, parse_early_negotiation_tlvs(), key_state::plaintext_read_buf, key_state::plaintext_write_buf, read_incoming_tls_ciphertext(), read_incoming_tls_plaintext(), key_state::rec_reliable, reliable_can_send(), reliable_empty(), reliable_get_entry_sequenced(), reliable_send(), S_ACTIVE, S_ERROR, S_ERROR_PRE, S_GOT_KEY, S_INITIAL, S_PRE_START, S_SENT_KEY, S_START, S_UNDEF, key_state::send_reliable, session_move_active(), session_move_pre_start(), key_state::state, status, tls_clear_error(), tls_x509_clear_env(), and write_control_auth().
Referenced by tls_process().
◆ tls_rec_payload()
Definition at line 4249 of file ssl.c.
References ASSERT, BLEN, buf_copy(), get_key_scan(), buffer::len, key_state::plaintext_read_buf, S_ACTIVE, key_state::state, and tls_clear_error().
Referenced by check_incoming_control_channel().
◆ tls_send_payload()
| bool tls_send_payload | ( | struct key_state * | ks, |
| const uint8_t * | data, | ||
| size_t | size ) |
Definition at line 4216 of file ssl.c.
References ASSERT, buffer_list_new(), buffer_list_push_data(), key_state_write_plaintext_const(), key_state::ks_ssl, key_state::paybuf, S_ACTIVE, key_state::state, and tls_clear_error().
Referenced by send_control_channel_string_dowork().
◆ tls_session_generate_data_channel_keys()
|
static |
Generate data channel keys for the supplied TLS session.
This erases the source material used to generate the data channel keys, and can thus be called only once per session.
Definition at line 1601 of file ssl.c.
References key_state::authenticated, cleanup(), key_state::crypto_options, D_TLS_ERRORS, crypto_options::flags, generate_key_expansion(), session::key, KEY_GEN_FAILED, KEY_GEN_OK, key_state::key_src, KS_AUTH_FALSE, KS_PRIMARY, msg, S_GENERATED_KEYS, secure_memzero(), key_state::state, tls_get_limit_aead(), and tls_limit_reneg_bytes().
Referenced by tls_multi_process(), and tls_session_update_crypto_params_do_work().
◆ tls_session_soft_reset()
| void tls_session_soft_reset | ( | struct tls_multi * | tls_multi | ) |
Definition at line 1833 of file ssl.c.
References key_state_soft_reset(), tls_multi::session, and TM_ACTIVE.
Referenced by process_incoming_dco().
◆ tls_session_update_crypto_params()
| bool tls_session_update_crypto_params | ( | struct tls_multi * | multi, |
| struct tls_session * | session, | ||
| struct options * | options, | ||
| struct frame * | frame, | ||
| struct frame * | frame_fragment, | ||
| struct link_socket_info * | lsi, | ||
| dco_context_t * | dco ) |
Update TLS session crypto parameters (cipher and auth) and derive data channel keys based on the supplied options.
Does nothing if keys are already generated.
- Parameters
-
multi The TLS object for this instance. session The TLS session to update. options The options to use when updating session. frame The frame options for this session (frame overhead is adjusted based on the selected cipher/auth). frame_fragment The fragment frame options. lsi link socket info to adjust MTU related options depending on the current protocol dco The dco context to perform dco_set_peer() whenever a crypto param update occurs.
- Returns
- true if updating succeeded or keys are already generated, false otherwise.
Definition at line 1705 of file ssl.c.
References check_session_cipher(), options::imported_protocol_flags, and tls_session_update_crypto_params_do_work().
Referenced by do_deferred_options_part2(), do_deferred_p2p_ncp(), and multi_client_generate_tls_keys().
◆ tls_session_update_crypto_params_do_work()
| bool tls_session_update_crypto_params_do_work | ( | struct tls_multi * | multi, |
| struct tls_session * | session, | ||
| struct options * | options, | ||
| struct frame * | frame, | ||
| struct frame * | frame_fragment, | ||
| struct link_socket_info * | lsi, | ||
| dco_context_t * | dco ) |
Definition at line 1633 of file ssl.c.
References options::authname, cipher_kt_mode_ofb_cfb(), options::ciphername, CO_PACKET_ID_LONG_FORM, CO_USE_DYNAMIC_TLS_CRYPT, D_DCO, D_MTU_INFO, dco_enabled(), tls_multi::dco_peer_id, dco_set_peer(), frame_calculate_dynamic(), frame_print(), init_key_type(), session::key, KEY_GEN_OK, KS_PRIMARY, msg, frame::mss_fix, options::ping_rec_timeout, options::ping_send_timeout, tls_session_generate_data_channel_keys(), and tls_session_generate_dynamic_tls_crypt_key().
Referenced by tls_session_update_crypto_params().
◆ tls_session_user_pass_enabled()
|
inlinestatic |
Returns whether or not the server should check for username/password.
- Parameters
-
session The current TLS session
- Returns
- true if username and password verification is enabled, false if not.
Definition at line 959 of file ssl.c.
References management_enable_def_auth(), and plugin_defined().
Referenced by key_method_2_read().
◆ tls_update_remote_addr()
| void tls_update_remote_addr | ( | struct tls_multi * | multi, |
| const struct link_socket_actual * | addr ) |
Updates remote address in TLS sessions.
- Parameters
-
multi - Tunnel to update addr - new address
Definition at line 4274 of file ssl.c.
References D_TLS_KEYSELECT, dmsg, gc, gc_free(), gc_new(), session::key, KS_SIZE, link_socket_actual_defined(), link_socket_actual_match(), print_link_socket_actual(), key_state::remote_addr, tls_multi::session, and TM_SIZE.
Referenced by multi_process_float().
◆ tls_version_parse()
| int tls_version_parse | ( | const char * | vstr, |
| const char * | extra ) |
Definition at line 434 of file ssl.c.
References TLS_VER_1_0, TLS_VER_1_1, TLS_VER_1_2, TLS_VER_1_3, TLS_VER_BAD, and tls_version_max().
Referenced by add_option().
◆ write_empty_string()
|
static |
Definition at line 1843 of file ssl.c.
References buf_write_u16().
Referenced by key_method_2_write(), and push_peer_info().
◆ write_outgoing_tls_ciphertext()
|
static |
Definition at line 2745 of file ssl.c.
References alloc_buf_gc(), ASSERT, buf_copy_n(), buf_len(), calc_control_channel_frame_overhead(), control_packet_needs_wkc(), D_TLS_DEBUG, D_TLS_ERRORS, dmsg, gc, gc_free(), gc_new(), INCR_GENERATED, session::key, key_state_read_ciphertext(), KS_PRIMARY, key_state::ks_ssl, buffer::len, max_int(), min_int(), msg, P_CONTROL_V1, P_CONTROL_WKC_V1, reliable_get_buf_output_sequenced(), reliable_get_num_output_sequenced_available(), reliable_mark_active_outgoing(), key_state::send_reliable, status, and TLS_CHANNEL_BUF_SIZE.
Referenced by check_outgoing_ciphertext().
◆ write_string()
|
static |
Definition at line 1853 of file ssl.c.
References buf_write(), and buf_write_u16().
Referenced by key_method_2_write(), and push_peer_info().
Variable Documentation
◆ auth_challenge
|
static |
Definition at line 292 of file ssl.c.
Referenced by auth_user_pass_mgmt(), auth_user_pass_setup(), get_user_pass_cr(), parse_auth_challenge(), ssl_purge_auth_challenge(), and ssl_put_auth_challenge().
◆ auth_token
|
static |
Definition at line 289 of file ssl.c.
Referenced by auth_user_pass_setup(), key_method_2_write(), ssl_clean_auth_token(), ssl_set_auth_token(), and ssl_set_auth_token_user().
◆ auth_user_pass
|
static |
Definition at line 288 of file ssl.c.
Referenced by auth_user_pass_setup(), key_method_2_write(), ssl_purge_auth(), and ssl_set_auth_nocache().
◆ auth_user_pass_enabled
|
static |
Definition at line 287 of file ssl.c.
Referenced by enable_auth_user_pass(), and key_method_2_write().
◆ passbuf
|
static |
Definition at line 254 of file ssl.c.
Referenced by pem_password_callback(), pem_password_setup(), ssl_get_auth_nocache(), ssl_purge_auth(), and ssl_set_auth_nocache().
Generated by
 1.15.0