#include <ssl_common.h>
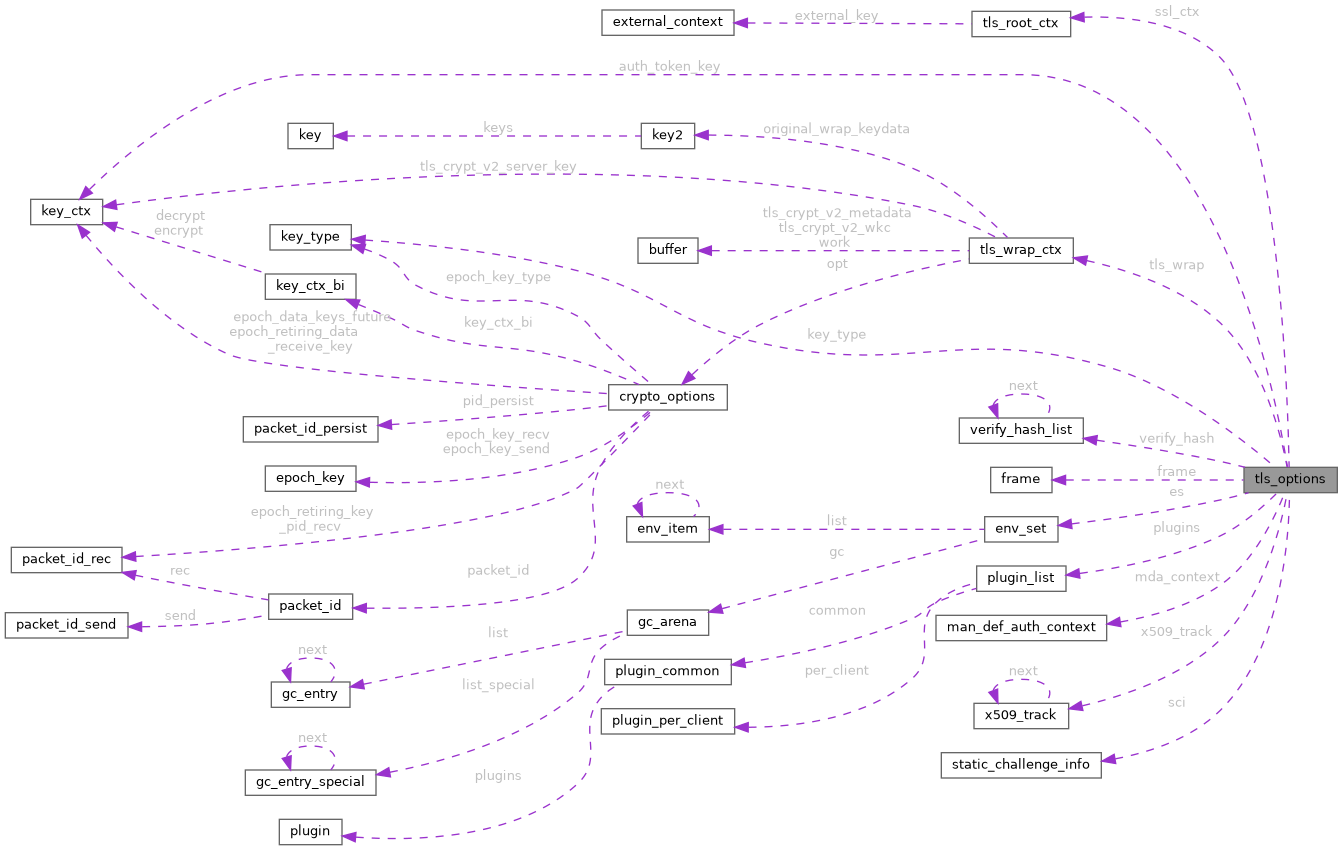
Data Fields | |
| struct tls_root_ctx * | ssl_ctx |
| struct key_type | key_type |
| bool | server |
| bool | xmit_hold |
| const char * | local_options |
| const char * | remote_options |
| bool | single_session |
| int | mode |
| bool | pull |
| int | push_peer_info_detail |
| The detail of info we push in peer info. | |
| int | transition_window |
| int | handshake_window |
| interval_t | packet_timeout |
| int64_t | renegotiate_bytes |
| int64_t | renegotiate_packets |
| uint64_t | aead_usage_limit |
| limit for AEAD cipher when not running in epoch data key mode, this is the sum of packets + blocks that are allowed to be used | |
| uint64_t | aead_usage_limit_override |
| Debug only option that allows overriding the usage limit This allows testing key rotation by using very small limits. | |
| interval_t | renegotiate_seconds |
| const char * | verify_command |
| int | verify_x509_type |
| const char * | verify_x509_name |
| const char * | crl_file |
| bool | crl_file_inline |
| int | ns_cert_type |
| unsigned | remote_cert_ku [MAX_PARMS] |
| const char * | remote_cert_eku |
| struct verify_hash_list * | verify_hash |
| int | verify_hash_depth |
| bool | verify_hash_no_ca |
| hash_algo_type | verify_hash_algo |
| char * | x509_username_field [MAX_PARMS] |
| unsigned int | crypto_flags |
| int | replay_window |
| int | replay_time |
| const char * | config_ciphername |
| const char * | config_ncp_ciphers |
| bool | data_epoch_supported |
| whether our underlying data channel supports new data channel features (epoch keys with AEAD tag at the end). | |
| bool | tls_crypt_v2 |
| const char * | tls_crypt_v2_verify_script |
| int | tls_crypt_v2_max_age |
| struct tls_wrap_ctx | tls_wrap |
| TLS handshake wrapping state. | |
| struct frame | frame |
| const char * | auth_user_pass_verify_script |
| const char * | client_crresponse_script |
| bool | auth_user_pass_verify_script_via_file |
| const char * | tmp_dir |
| const char * | export_peer_cert_dir |
| const char * | auth_user_pass_file |
| bool | auth_user_pass_file_inline |
| bool | auth_user_pass_username_only |
| bool | auth_token_generate |
| Generate auth-tokens on successful user/pass auth,seet via options->auth_token_generate. | |
| bool | auth_token_call_auth |
| always call normal authentication | |
| unsigned int | auth_token_lifetime |
| unsigned int | auth_token_renewal |
| struct key_ctx | auth_token_key |
| const char * | client_config_dir_exclusive |
| struct env_set * | es |
| openvpn_net_ctx_t * | net_ctx |
| const struct plugin_list * | plugins |
| unsigned int | ssl_flags |
| struct man_def_auth_context * | mda_context |
| const struct x509_track * | x509_track |
| const struct static_challenge_info * | sci |
| int | gremlin |
| const char * | ekm_label |
| size_t | ekm_label_size |
| size_t | ekm_size |
| bool | dco_enabled |
| Whether keys have to be installed in DCO or not. | |
Detailed Description
Definition at line 305 of file ssl_common.h.
Field Documentation
◆ aead_usage_limit
| uint64_t tls_options::aead_usage_limit |
limit for AEAD cipher when not running in epoch data key mode, this is the sum of packets + blocks that are allowed to be used
Definition at line 348 of file ssl_common.h.
◆ aead_usage_limit_override
| uint64_t tls_options::aead_usage_limit_override |
Debug only option that allows overriding the usage limit This allows testing key rotation by using very small limits.
Definition at line 353 of file ssl_common.h.
Referenced by do_init_crypto_tls(), and init_epoch_keys().
◆ auth_token_call_auth
| bool tls_options::auth_token_call_auth |
always call normal authentication
Definition at line 408 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ auth_token_generate
| bool tls_options::auth_token_generate |
Generate auth-tokens on successful user/pass auth,seet via options->auth_token_generate.
Definition at line 405 of file ssl_common.h.
Referenced by add_session_token_env(), do_init_crypto_tls(), and setup().
◆ auth_token_key
| struct key_ctx tls_options::auth_token_key |
Definition at line 412 of file ssl_common.h.
Referenced by auth_token_fail_invalid_key(), auth_token_test_key_load(), auth_token_test_random_keys(), do_init_crypto_tls(), generate_auth_token(), setup(), teardown(), and verify_auth_token().
◆ auth_token_lifetime
| unsigned int tls_options::auth_token_lifetime |
Definition at line 409 of file ssl_common.h.
Referenced by auth_token_test_timeout(), do_init_crypto_tls(), setup(), and verify_auth_token().
◆ auth_token_renewal
| unsigned int tls_options::auth_token_renewal |
Definition at line 410 of file ssl_common.h.
Referenced by auth_token_test_timeout(), do_init_crypto_tls(), and setup().
◆ auth_user_pass_file
| const char* tls_options::auth_user_pass_file |
Definition at line 401 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ auth_user_pass_file_inline
| bool tls_options::auth_user_pass_file_inline |
Definition at line 402 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ auth_user_pass_username_only
| bool tls_options::auth_user_pass_username_only |
Definition at line 403 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ auth_user_pass_verify_script
| const char* tls_options::auth_user_pass_verify_script |
Definition at line 396 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ auth_user_pass_verify_script_via_file
| bool tls_options::auth_user_pass_verify_script_via_file |
Definition at line 398 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ client_config_dir_exclusive
| const char* tls_options::client_config_dir_exclusive |
Definition at line 415 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ client_crresponse_script
| const char* tls_options::client_crresponse_script |
Definition at line 397 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ config_ciphername
| const char* tls_options::config_ciphername |
Definition at line 377 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ config_ncp_ciphers
| const char* tls_options::config_ncp_ciphers |
Definition at line 378 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ crl_file
| const char* tls_options::crl_file |
Definition at line 360 of file ssl_common.h.
Referenced by do_init_crypto_tls(), tls_verify_crl_missing(), and verify_cert().
◆ crl_file_inline
| bool tls_options::crl_file_inline |
Definition at line 361 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ crypto_flags
| unsigned int tls_options::crypto_flags |
Definition at line 372 of file ssl_common.h.
Referenced by do_init_crypto_tls(), and init_key_contexts().
◆ data_epoch_supported
| bool tls_options::data_epoch_supported |
whether our underlying data channel supports new data channel features (epoch keys with AEAD tag at the end).
This is always true for the internal implementation but can be false for DCO implementations
Definition at line 384 of file ssl_common.h.
Referenced by do_init_crypto_tls(), and multi_client_set_protocol_options().
◆ dco_enabled
| bool tls_options::dco_enabled |
Whether keys have to be installed in DCO or not.
Definition at line 459 of file ssl_common.h.
Referenced by do_init_crypto_tls(), p2p_ncp_set_options(), and tls_multi_init_finalize().
◆ ekm_label
| const char* tls_options::ekm_label |
Definition at line 455 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ ekm_label_size
| size_t tls_options::ekm_label_size |
Definition at line 456 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ ekm_size
| size_t tls_options::ekm_size |
Definition at line 457 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ es
| struct env_set* tls_options::es |
Definition at line 418 of file ssl_common.h.
Referenced by do_init_crypto_tls(), key_state_gen_auth_control_files(), and verify_cert().
◆ export_peer_cert_dir
| const char* tls_options::export_peer_cert_dir |
Definition at line 400 of file ssl_common.h.
Referenced by do_init_crypto_tls(), and verify_cert().
◆ frame
| struct frame tls_options::frame |
Definition at line 393 of file ssl_common.h.
Referenced by do_init_frame_tls(), test_tls_crypt_secure_reneg_key(), tls_auth_standalone_init(), tls_multi_init_finalize(), and tls_process().
◆ gremlin
| int tls_options::gremlin |
Definition at line 452 of file ssl_common.h.
Referenced by do_init_crypto_tls(), and tls_multi_process().
◆ handshake_window
| int tls_options::handshake_window |
Definition at line 342 of file ssl_common.h.
Referenced by auth_deferred_expire_window(), do_init_crypto_tls(), and send_auth_pending_messages().
◆ key_type
| struct key_type tls_options::key_type |
Definition at line 313 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ local_options
| const char* tls_options::local_options |
Definition at line 323 of file ssl_common.h.
Referenced by tls_multi_init_set_options().
◆ mda_context
| struct man_def_auth_context* tls_options::mda_context |
Definition at line 442 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ mode
| int tls_options::mode |
Definition at line 328 of file ssl_common.h.
Referenced by do_init_crypto_tls(), and tls_multi_init_finalize().
◆ net_ctx
| openvpn_net_ctx_t* tls_options::net_ctx |
Definition at line 419 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ ns_cert_type
| int tls_options::ns_cert_type |
Definition at line 362 of file ssl_common.h.
Referenced by do_init_crypto_tls(), and verify_peer_cert().
◆ packet_timeout
| interval_t tls_options::packet_timeout |
Definition at line 343 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ plugins
| const struct plugin_list* tls_options::plugins |
Definition at line 420 of file ssl_common.h.
Referenced by do_init_crypto_tls(), and verify_cert().
◆ pull
| bool tls_options::pull |
Definition at line 329 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ push_peer_info_detail
| int tls_options::push_peer_info_detail |
The detail of info we push in peer info.
0 - nothing at all, P2MP server only 1 - only the most basic information to negotiate cipher and features for P2P NCP 2 - normal setting for clients 3 - full information including "sensitive data" like IV_HWADDR enabled by –push-peer-info
Definition at line 340 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ remote_cert_eku
| const char* tls_options::remote_cert_eku |
Definition at line 364 of file ssl_common.h.
Referenced by do_init_crypto_tls(), and verify_peer_cert().
◆ remote_cert_ku
| unsigned tls_options::remote_cert_ku[MAX_PARMS] |
Definition at line 363 of file ssl_common.h.
Referenced by do_init_crypto_tls(), and verify_peer_cert().
◆ remote_options
| const char* tls_options::remote_options |
Definition at line 324 of file ssl_common.h.
Referenced by tls_multi_init_set_options().
◆ renegotiate_bytes
| int64_t tls_options::renegotiate_bytes |
Definition at line 344 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ renegotiate_packets
| int64_t tls_options::renegotiate_packets |
Definition at line 345 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ renegotiate_seconds
| interval_t tls_options::renegotiate_seconds |
Definition at line 354 of file ssl_common.h.
Referenced by auth_deferred_expire_window(), do_init_crypto_tls(), send_auth_pending_messages(), and setup().
◆ replay_time
| int tls_options::replay_time |
Definition at line 375 of file ssl_common.h.
Referenced by do_init_crypto_tls(), test_tls_crypt_secure_reneg_key(), and tls_auth_standalone_init().
◆ replay_window
| int tls_options::replay_window |
Definition at line 374 of file ssl_common.h.
Referenced by do_init_crypto_tls(), test_tls_crypt_secure_reneg_key(), and tls_auth_standalone_init().
◆ sci
| const struct static_challenge_info* tls_options::sci |
Definition at line 448 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ server
| bool tls_options::server |
Definition at line 316 of file ssl_common.h.
Referenced by do_init_crypto_tls(), and tls_pre_decrypt().
◆ single_session
| bool tls_options::single_session |
Definition at line 327 of file ssl_common.h.
Referenced by do_init_crypto_tls(), tls_multi_process(), tls_pre_decrypt(), and tls_set_single_session().
◆ ssl_ctx
| struct tls_root_ctx* tls_options::ssl_ctx |
Definition at line 310 of file ssl_common.h.
Referenced by do_init_crypto_tls(), and tls_verify_crl_missing().
◆ ssl_flags
| unsigned int tls_options::ssl_flags |
Definition at line 439 of file ssl_common.h.
Referenced by do_init_crypto_tls(), tls_verify_crl_missing(), and verify_cert().
◆ tls_crypt_v2
| bool tls_options::tls_crypt_v2 |
Definition at line 386 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ tls_crypt_v2_max_age
| int tls_options::tls_crypt_v2_max_age |
Definition at line 388 of file ssl_common.h.
Referenced by do_init_crypto_tls(), and tls_crypt_v2_extract_client_key().
◆ tls_crypt_v2_verify_script
| const char* tls_options::tls_crypt_v2_verify_script |
Definition at line 387 of file ssl_common.h.
Referenced by do_init_crypto_tls(), tls_crypt_v2_extract_client_key(), tls_crypt_v2_unwrap_checks(), and tls_crypt_v2_verify_metadata().
◆ tls_wrap
| struct tls_wrap_ctx tls_options::tls_wrap |
TLS handshake wrapping state.
Definition at line 391 of file ssl_common.h.
Referenced by do_init_crypto_tls(), and tls_auth_standalone_init().
◆ tmp_dir
| const char* tls_options::tmp_dir |
Definition at line 399 of file ssl_common.h.
Referenced by do_init_crypto_tls(), key_state_gen_auth_control_files(), tls_crypt_v2_unwrap_checks(), and tls_crypt_v2_verify_metadata().
◆ transition_window
| int tls_options::transition_window |
Definition at line 341 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ verify_command
| const char* tls_options::verify_command |
Definition at line 357 of file ssl_common.h.
Referenced by do_init_crypto_tls(), and verify_cert().
◆ verify_hash
| struct verify_hash_list* tls_options::verify_hash |
Definition at line 365 of file ssl_common.h.
Referenced by do_init_crypto_tls(), and verify_cert().
◆ verify_hash_algo
| hash_algo_type tls_options::verify_hash_algo |
Definition at line 368 of file ssl_common.h.
Referenced by do_init_crypto_tls(), and verify_cert().
◆ verify_hash_depth
| int tls_options::verify_hash_depth |
Definition at line 366 of file ssl_common.h.
Referenced by do_init_crypto_tls(), and verify_cert().
◆ verify_hash_no_ca
| bool tls_options::verify_hash_no_ca |
Definition at line 367 of file ssl_common.h.
Referenced by do_init_crypto_tls().
◆ verify_x509_name
| const char* tls_options::verify_x509_name |
Definition at line 359 of file ssl_common.h.
Referenced by do_init_crypto_tls(), and verify_peer_cert().
◆ verify_x509_type
| int tls_options::verify_x509_type |
Definition at line 358 of file ssl_common.h.
Referenced by do_init_crypto_tls(), and verify_peer_cert().
◆ x509_track
| const struct x509_track* tls_options::x509_track |
Definition at line 445 of file ssl_common.h.
Referenced by do_init_crypto_tls(), and verify_cert().
◆ x509_username_field
| char* tls_options::x509_username_field[MAX_PARMS] |
Definition at line 369 of file ssl_common.h.
Referenced by do_init_crypto_tls(), and verify_cert().
◆ xmit_hold
| bool tls_options::xmit_hold |
Definition at line 319 of file ssl_common.h.
Referenced by do_init_crypto_tls().
The documentation for this struct was generated from the following file:
- src/openvpn/ssl_common.h
Generated by
 1.15.0