Data Channel Cryptography OpenSSL-specific backend interface. More...
#include <openssl/evp.h>#include <openssl/hmac.h>#include <openssl/md5.h>#include <openssl/sha.h>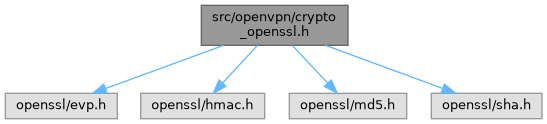
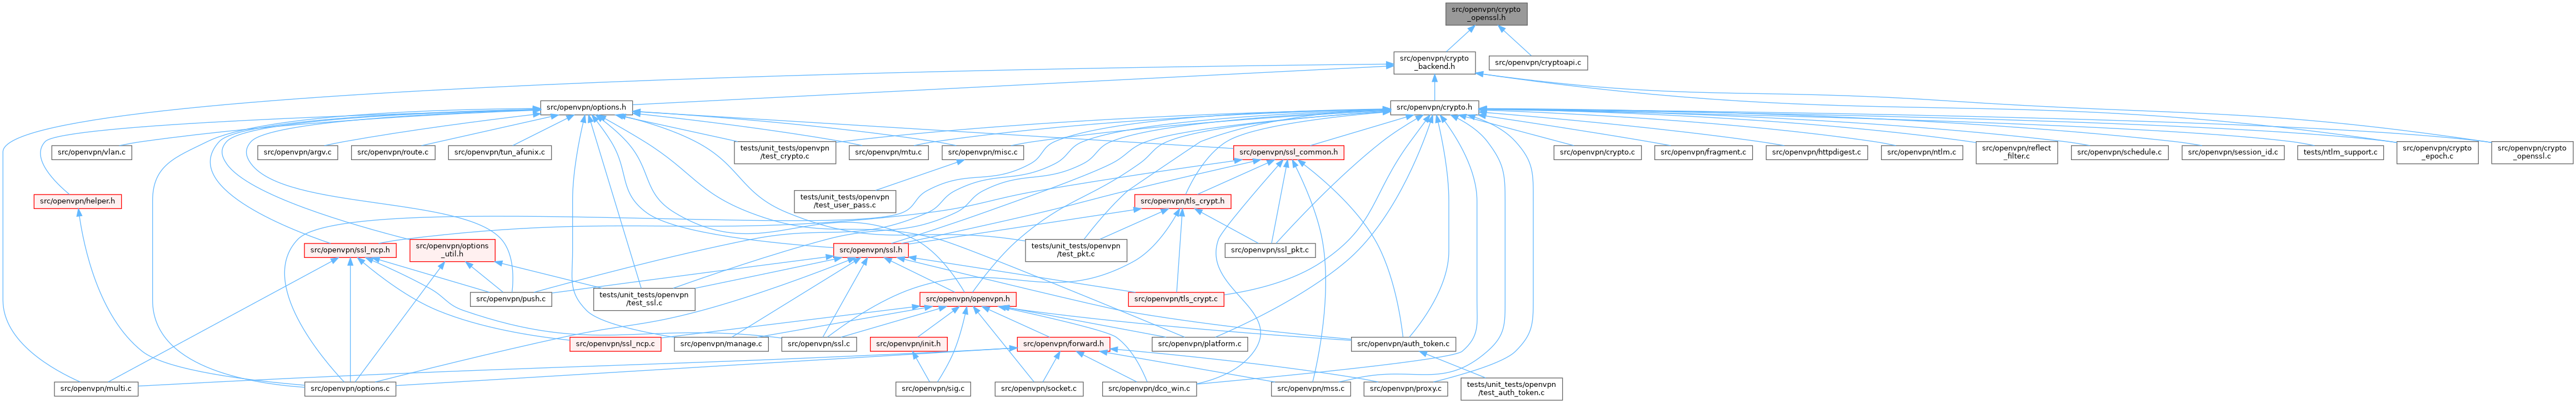
Go to the source code of this file.
Macros | |
| #define | OPENVPN_MAX_IV_LENGTH EVP_MAX_IV_LENGTH |
| Maximum length of an IV. | |
| #define | OPENVPN_MODE_CBC EVP_CIPH_CBC_MODE |
| Cipher is in CBC mode. | |
| #define | OPENVPN_MODE_OFB EVP_CIPH_OFB_MODE |
| Cipher is in OFB mode. | |
| #define | OPENVPN_MODE_CFB EVP_CIPH_CFB_MODE |
| Cipher is in CFB mode. | |
| #define | OPENVPN_MODE_GCM EVP_CIPH_GCM_MODE |
| Cipher is in GCM mode. | |
| #define | OPENVPN_OP_ENCRYPT 1 |
| Cipher should encrypt. | |
| #define | OPENVPN_OP_DECRYPT 0 |
| Cipher should decrypt. | |
| #define | MD4_DIGEST_LENGTH 16 |
| #define | crypto_msg(flags, ...) |
| Retrieve any OpenSSL errors, then print the supplied error message. | |
Typedefs | |
| typedef EVP_CIPHER_CTX | cipher_ctx_t |
| Generic cipher context. | |
| typedef EVP_MD_CTX | md_ctx_t |
| Generic message digest context. | |
| typedef HMAC_CTX | hmac_ctx_t |
| Generic HMAC context. | |
| typedef const EVP_CIPHER | evp_cipher_type |
| typedef const EVP_MD | evp_md_type |
Functions | |
| void | crypto_print_openssl_errors (const unsigned int flags) |
| Retrieve any occurred OpenSSL errors and print those errors. | |
Detailed Description
Data Channel Cryptography OpenSSL-specific backend interface.
Definition in file crypto_openssl.h.
Macro Definition Documentation
◆ crypto_msg
| #define crypto_msg | ( | flags, | |
| ... ) |
Retrieve any OpenSSL errors, then print the supplied error message.
This is just a convenience wrapper for often occurring situations.
- Parameters
-
flags Flags to indicate error type and priority. ... Format string and optional format arguments
Definition at line 116 of file crypto_openssl.h.
Referenced by backend_tls_ctx_reload_crl(), backend_x509_write_pem(), bio_read(), bio_write(), cipher_ctx_init(), cipher_ctx_update(), cipher_ctx_update_ad(), cipher_valid_reason(), crypto_load_provider(), crypto_pem_decode(), crypto_unload_provider(), hmac_ctx_init(), hmac_ctx_reset(), key_state_ssl_init(), md_ctx_init(), md_get(), rand_bytes(), show_available_curves(), show_available_tls_ciphers_list(), tls_ctx_add_extra_certs(), tls_ctx_load_ca(), tls_ctx_load_cert_pem_file(), tls_ctx_load_cert_uri(), tls_ctx_load_cryptoapi(), tls_ctx_load_dh_params(), tls_ctx_load_ecdh_params(), tls_ctx_load_extra_certs(), tls_ctx_load_pkcs12(), tls_ctx_load_priv_file(), tls_ctx_new(), tls_ctx_restrict_ciphers(), tls_ctx_restrict_ciphers_tls13(), tls_ctx_set_tls_groups(), and tls_ctx_use_management_external_key().
◆ MD4_DIGEST_LENGTH
| #define MD4_DIGEST_LENGTH 16 |
Definition at line 97 of file crypto_openssl.h.
◆ OPENVPN_MAX_IV_LENGTH
| #define OPENVPN_MAX_IV_LENGTH EVP_MAX_IV_LENGTH |
Maximum length of an IV.
Definition at line 75 of file crypto_openssl.h.
◆ OPENVPN_MODE_CBC
| #define OPENVPN_MODE_CBC EVP_CIPH_CBC_MODE |
Cipher is in CBC mode.
Definition at line 78 of file crypto_openssl.h.
◆ OPENVPN_MODE_CFB
| #define OPENVPN_MODE_CFB EVP_CIPH_CFB_MODE |
Cipher is in CFB mode.
Definition at line 84 of file crypto_openssl.h.
◆ OPENVPN_MODE_GCM
| #define OPENVPN_MODE_GCM EVP_CIPH_GCM_MODE |
Cipher is in GCM mode.
Definition at line 87 of file crypto_openssl.h.
◆ OPENVPN_MODE_OFB
| #define OPENVPN_MODE_OFB EVP_CIPH_OFB_MODE |
Cipher is in OFB mode.
Definition at line 81 of file crypto_openssl.h.
◆ OPENVPN_OP_DECRYPT
| #define OPENVPN_OP_DECRYPT 0 |
Cipher should decrypt.
Definition at line 95 of file crypto_openssl.h.
◆ OPENVPN_OP_ENCRYPT
| #define OPENVPN_OP_ENCRYPT 1 |
Cipher should encrypt.
Definition at line 92 of file crypto_openssl.h.
Typedef Documentation
◆ cipher_ctx_t
| typedef EVP_CIPHER_CTX cipher_ctx_t |
Generic cipher context.
Definition at line 41 of file crypto_openssl.h.
◆ evp_cipher_type
| typedef const EVP_CIPHER evp_cipher_type |
Definition at line 67 of file crypto_openssl.h.
◆ evp_md_type
| typedef const EVP_MD evp_md_type |
Definition at line 68 of file crypto_openssl.h.
◆ hmac_ctx_t
| typedef HMAC_CTX hmac_ctx_t |
Generic HMAC context.
Definition at line 48 of file crypto_openssl.h.
◆ md_ctx_t
| typedef EVP_MD_CTX md_ctx_t |
Generic message digest context.
Definition at line 44 of file crypto_openssl.h.
Function Documentation
◆ crypto_print_openssl_errors()
| void crypto_print_openssl_errors | ( | const unsigned int | flags | ) |
Retrieve any occurred OpenSSL errors and print those errors.
Note that this function uses the not thread-safe OpenSSL error API.
- Parameters
-
flags Flags to indicate error type and priority.
Definition at line 231 of file crypto_openssl.c.
References check_debug_level(), D_CRYPT_ERRORS, D_TLS_DEBUG_MED, ERR_get_error_all(), and msg.
Referenced by tls_ctx_load_cert_pem_file(), tls_ctx_load_cert_uri(), and tls_ctx_load_pkcs12().
Generated by
 1.15.0